//First look
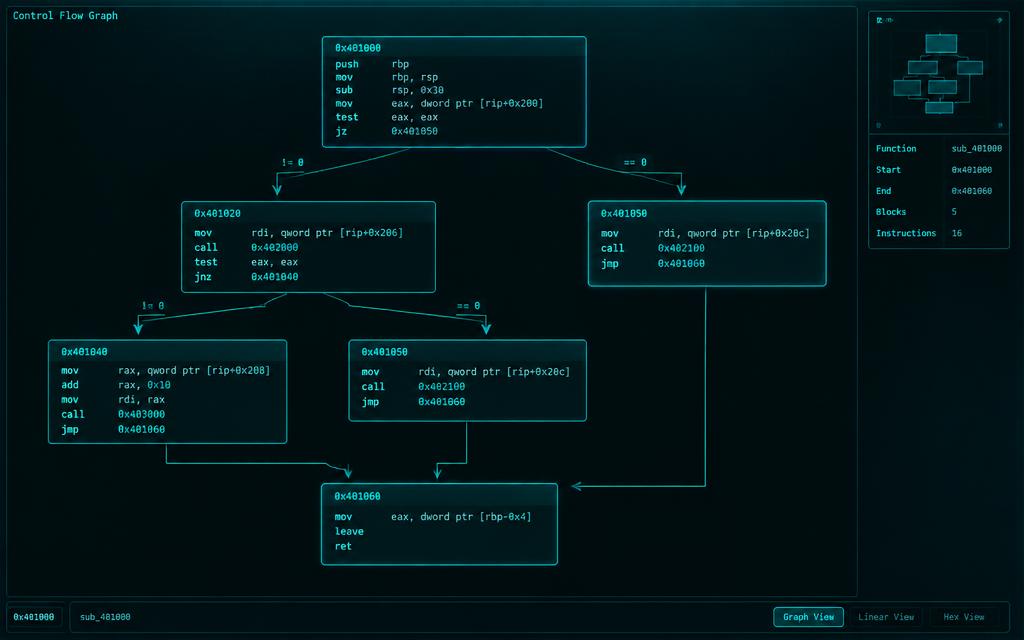
Binary terlihat kecil tapi penuh instruksi aneh — tanda klasik packer custom. Entry point hanya berisi loop decrypt yang menulis ke region RWX lalu jump ke sana.
//Dumping the unpacked code
Daripada reversing stub-nya secara statis, kita jalankan di gdb, break tepat setelah loop decrypt, lalu dump memory region-nya.
// bash
(gdb) break *0x4012f4
(gdb) run
(gdb) dump binary memory unpacked.bin 0x403000 0x404800//The key check
Hasil dump berisi fungsi check yang melakukan XOR input dengan key 0x5A lalu membandingkan dengan tabel byte. Tinggal balik operasinya:
// python
table = [0x3c, 0x2b, 0x3e, 0x36, 0x29, 0x31, ...]
flag = "".join(chr(b ^ 0x5A) for b in table)
print(flag)  # COMPFEST{unp4ck3d_4nd_pwn3d}